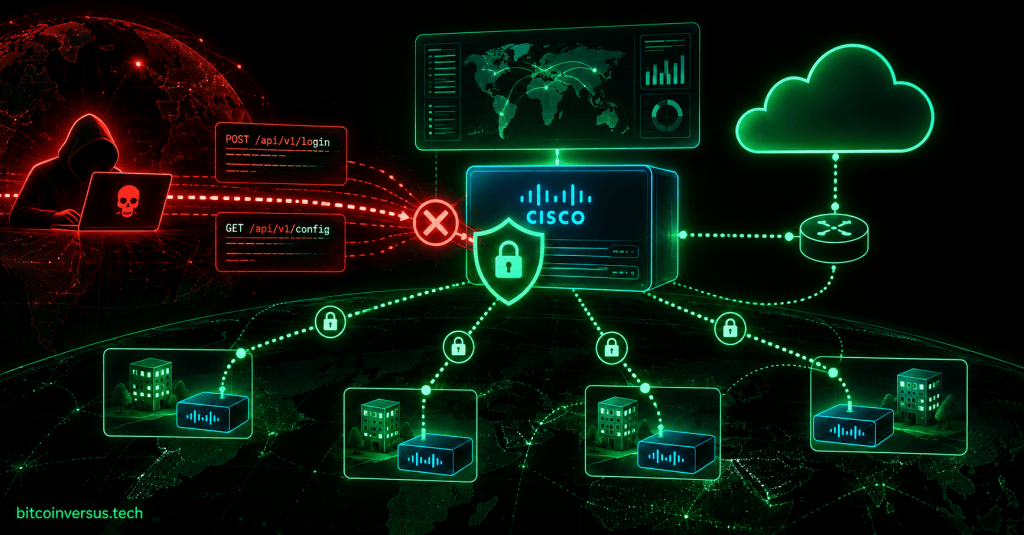
Cisco has patched an actively exploited authentication-bypass vulnerability in Catalyst SD-WAN Manager that can allow an unauthenticated remote attacker to reach an affected system with administrator privileges.
In its September 30 security advisory, Cisco assigned CVE-2026-76504 a CVSS score of 9.8 and said the issue stems from improper handling of URI encoding in HTTP requests. Cisco says there are no workarounds and strongly recommends upgrading to a fixed release.
Why this is a network-security problem
SD-WAN Manager sits at a sensitive point in enterprise networking because it coordinates policy, visibility and control across distributed WAN infrastructure. If that management layer can be reached without authentication, the risk is not limited to a single edge device; the attacker may gain access to administrative functions that influence the wider WAN environment.
Independent reporting from SecurityWeek confirms that Cisco patched the flaw after exploitation was observed in the wild and that fixed releases are now available across supported Catalyst SD-WAN branches.
The issue also reinforces why segmentation remains one of the most important network-defense fundamentals. BitcoinVersus recently covered VLAN basics and logical segmentation, which help reduce how freely traffic and administrative access can move across an environment when one control plane becomes exposed.
Cisco says exploitation was already happening
Cisco says its Product Security Incident Response Team became aware of active exploitation in September 2026 while resolving a Technical Assistance Center case. The advisory includes indicators defenders can hunt for in vmanage-server.log, including suspicious requests involving encoded j_security_check paths and reserved user names.
For defenders, that makes packet inspection and log review especially important. BitcoinVersus has a separate guide on packet capture and network traffic inspection, which covers the operational side of examining traffic when behavior on a management plane does not look normal.
The SD-WAN security model still depends on the management plane
Cisco’s own SD-WAN Secure Fabric overview shows how the platform is designed to centralize security policy, threat protection and visibility across the WAN. That architecture is exactly why a management-layer authentication bypass is so serious: the security controls may be distributed, but the orchestration point remains highly privileged.
The same principle is why firewalls and access controls need layered deployment instead of being treated as a single perimeter. BitcoinVersus has previously covered firewall fundamentals, including how rule enforcement at network boundaries complements segmentation and monitoring.
What administrators need to do
Cisco says there is no configuration workaround for CVE-2026-76504. Organizations running affected Catalyst SD-WAN Manager releases need to upgrade to a fixed software version and review logs for signs of unauthorized authentication attempts.
The fixed branches listed by Cisco include 20.9.10.1, 20.12.8.2, 20.15.6.1, 20.18.4.1, 26.1.2.1 and 26.2.1. Cisco-managed SD-WAN deployments have already been patched.
The broader lesson is simple: software-defined networking may centralize policy and simplify operations, but it also concentrates privilege. A management-plane vulnerability with unauthenticated administrative access deserves the same urgency as a critical firewall or VPN gateway flaw because one successful compromise can expose far more than a single node.
BitcoinVersus.Tech
Advertisement
Editor’s Note:
We volunteer daily to ensure the credibility of the information on this platform is Verifiably True. If you would like to support to help further secure the integrity of our research initiatives, please donate here: 3C9o19EH5HSiwEPyCTmEKzxhNCbo2X6TTb
BitcoinVersus.tech is not a financial advisor. This media platform reports on financial subjects purely for informational purposes.


Leave a comment