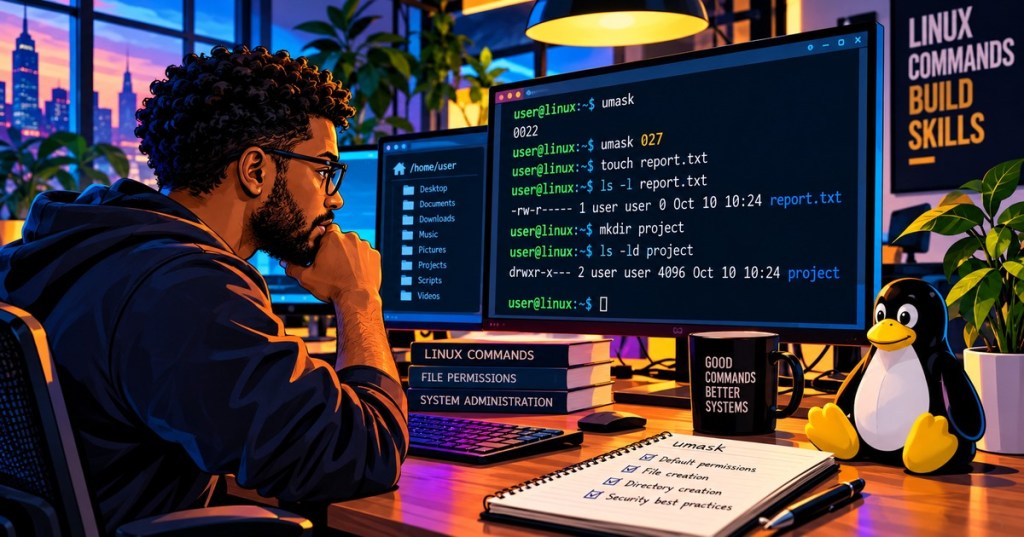
The umask command controls which permission bits are removed when new files and directories are created. It follows directly from Linux Command #50 – chmod: chmod changes permissions that already exist, while umask influences the defaults applied at creation time.
What umask does
Run umask with no arguments to print the current mask. Run umask -S to display the effective allowed permissions symbolically. A value such as 0022 means that group write and other write permissions are masked off when a program creates a file or directory.
The underlying rule is not ordinary subtraction. Linux clears permission bits selected by the mask. In bitwise form, the resulting mode is the program’s requested mode combined with the inverse of the mask. The Linux umask manual page describes this as permissions being turned off from the mode requested by file-creation system calls.

Why files and directories start differently
Programs commonly request a starting mode of 666 for ordinary files and 777 for directories. The difference matters because normal new files are not automatically executable. A umask can remove permissions, but it does not add execute permission that the creating program never requested.
With umask 022, a typical file requested as 666 becomes 644, while a directory requested as 777 becomes 755. With umask 027, those typical results become 640 for files and 750 for directories.
Check the current mask before changing it
Start with umask. If the shell prints 0022, record that value before experimenting. Then create a disposable test directory and file with mkdir umask-lab and touch umask-lab/test.txt. Inspect them with ls -ld umask-lab umask-lab/test.txt.
For a temporary test in the current shell, run umask 027, create a new file and directory, and inspect their permissions. When finished, restore the original mask you recorded. A shell-level umask change normally affects that shell and programs launched from it; it does not retroactively change existing files.
Symbolic notation
umask -S shows the allowed permissions in symbolic form. For example, a mask equivalent to 022 commonly displays u=rwx,g=rx,o=rx. This is often easier to read than octal notation when you are learning the relationship between users, groups, and others.
umask does not replace chmod
umask affects permissions when new objects are created. chmod changes the permissions on an existing file or directory. If touch report.txt creates a file as 644 because of your current mask, changing the mask later will not alter report.txt. You would use chmod for that existing file.
This also connects to ownership. Linux Command #49 – chown changes the owner, while Linux Command #48 – chgrp changes group ownership. Together, chown, chgrp, chmod, and umask form a core Linux permissions toolkit.
Default ACLs can change the result
If the parent directory has a default access-control list, the resulting permissions may not match the simple umask examples above. The Linux manual notes that a default ACL can take precedence over the process umask for inherited permissions. When the result looks unexpected, inspect the directory with getfacl DIRECTORY and look for entries beginning with default:.
Practice lab
- Run
umaskand record the current value. - Create
lab-file-awithtouchandlab-dir-awithmkdir. - Inspect both with
ls -ld. - Temporarily run
umask 027. - Create
lab-file-bandlab-dir-b. - Compare the permissions of the A and B objects.
- Restore the original mask before leaving the shell.
Knowledge check
- What does
umaskcontrol? - What typical file permission results from a requested mode of
666withumask 022? - What typical directory permission results from
777withumask 027? - Can changing
umaskmodify a file that already exists? - Why does
umask 000not automatically make a normal new file executable?
Answer guide
- It controls which permission bits are masked off when new files and directories are created.
- Typically
644. - Typically
750. - No. Use
chmodto change permissions on an existing object. - Because ordinary file-creation tools commonly request
666, which contains no execute bits for the mask to preserve.
Key takeaway
umask sets a permission filter for newly created files and directories; chmod edits permissions after creation. Check the current mask before changing it, test in a disposable location, and remember that ACLs or service-specific settings can affect the final permissions.
Advertisement
BitcoinVersus.Tech Editor’s Note:
We volunteer daily to ensure the credibility of the information on this platform is Verifiably True. If you would like to support to help further secure the integrity of our research initiatives, please donate here: 3C9o19EH5HSiwEPyCTmEKzxhNCbo2X6TTb
BitcoinVersus.tech is not a financial advisor. This media platform reports on financial subjects purely for informational purposes.


Leave a Reply