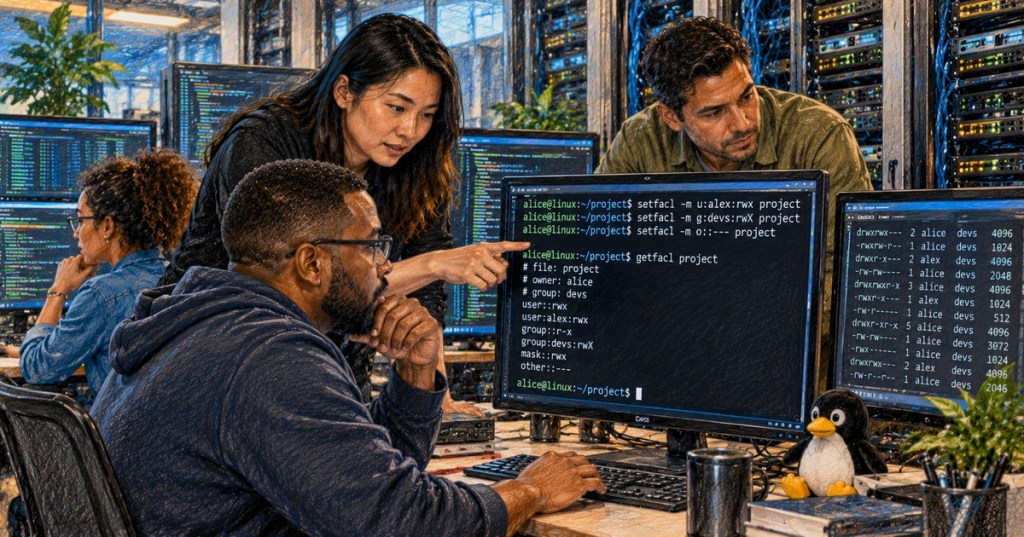
setfacl modifies Linux Access Control Lists so you can grant or remove permissions for specific users and groups without changing a file’s owner or relying only on the traditional owner/group/other model. It is the direct companion to Linux Command #52 – getfacl, which reads ACLs.
What setfacl changes
Traditional Linux permissions give one set of permissions to the owner, one to the owning group, and one to everyone else. ACLs add finer-grained entries. With setfacl, you can give one additional user read access, grant a project group write access, create inherited defaults on a directory, or remove extended ACL entries later.
The Linux setfacl(1) manual defines -m as modify, -x as remove, -b as remove all extended entries, and -d as applying operations to a directory’s default ACL. The file owner or a process with the required privilege can modify the ACL.
getfacl and setfacl, including named users, recursive changes, and default ACLs.Grant a named user access
To give a user named Alice read access to report.txt, run setfacl -m u:alice:r report.txt. The u: field identifies a user entry, alice is the account name, and r is the permission being granted.
To grant read and write access instead, use setfacl -m u:alice:rw report.txt. Verify the result with getfacl report.txt. The new named-user entry should appear separately from user::, which represents the file owner.
Grant a named group access
A named group uses the g: form. For example, setfacl -m g:developers:rwx project grants the developers group read, write, and execute permissions on the directory itself. Remember that directory execute permission means search/traverse permission; it is required to enter or access objects through that directory.
This is where ACLs extend the ideas from Linux Command #50 – chmod. chmod remains the normal tool for owner/group/other mode bits, while setfacl is useful when the access model needs specific additional users or groups.
The ACL mask can limit effective permissions
Extended ACLs include an effective-rights mask. The mask limits the permissions available to named users, the owning group, and named groups. That means a named entry can contain rwx while the effective access is smaller because the mask is more restrictive.
By default, setfacl recalculates the mask when needed. The -n or --no-mask option suppresses that recalculation. Do not use -n casually; a stale mask is a common reason an ACL looks correct but does not grant the access an administrator expected.
setfacl, getfacl, masks, named entries, and default ACL behavior.Remove one ACL entry
Use -x to remove a specific named entry. For example, setfacl -x u:alice report.txt removes Alice’s named-user ACL entry. When removing an entry, you identify the entry but do not include a permission field.
For a named group, the equivalent form is setfacl -x g:developers project. Always verify with getfacl afterward instead of assuming the command produced the intended ACL.
Remove all extended ACL entries
setfacl -b FILE removes all extended ACL entries while retaining the base owner, group, and other entries. This is useful when returning a file to the ordinary permission model, but it is broader than deleting one named user or group entry, so inspect the ACL before using it on production data.
Create default ACLs on directories
Default ACLs act as an inheritance template for newly created objects inside a directory. For example, setfacl -d -m g:developers:rwx shared adds a default entry for the developers group to the shared directory.
This does not rewrite every existing file under the directory. It affects the ACL inherited by newly created children. To inspect the directory’s defaults, use getfacl -d shared. This also connects directly to Linux Command #51 – umask: default ACLs participate in determining the final permissions of new files and directories.
Recursive ACL changes
setfacl -R -m g:developers:rX project applies a group ACL recursively. The capital X is useful in recursive permission work because it grants execute only to directories or to files that already have execute permission for some user. That helps avoid turning ordinary data files into executable files simply because a recursive rule was applied.
Recursive changes can affect thousands of objects very quickly. Test the exact command on a disposable tree first, capture the current ACLs when rollback matters, and avoid experimenting against system directories.
Back up and restore ACLs
The output from getfacl can be used as input to setfacl. For a directory tree, administrators can create a permissions backup with a recursive getfacl command and restore it later using setfacl --restore=FILE. This is useful before large ACL migrations because the backup can preserve more than a simple list of mode bits.
Useful setfacl commands
setfacl -m u:alice:r FILE— give Alice read access.setfacl -m g:developers:rw FILE— give the developers group read/write access.setfacl -x u:alice FILE— remove Alice’s named-user entry.setfacl -b FILE— remove all extended ACL entries.setfacl -k DIRECTORY— remove the directory’s default ACL.setfacl -d -m g:developers:rwx DIRECTORY— add a default group ACL.setfacl -R -m g:developers:rX DIRECTORY— modify ACLs recursively using conditional execute.setfacl -m m::rx FILE— explicitly set the effective-rights mask.
Troubleshooting checklist
- Run
getfacl TARGETbefore changing anything. - Confirm the correct user or group name with
getentorid. - Apply the smallest ACL change needed.
- Run
getfacl TARGETagain and inspect the mask and effective rights. - Check execute/search permission on every parent directory if access still fails.
- Remember that ACLs do not change file ownership; use
chownwhen ownership itself is wrong. - Test access as the affected user when possible instead of relying only on the ACL listing.
Practice lab
- Create a disposable directory named
acl-laband a file inside it. - Run
getfaclon both objects and save the initial output. - Add a named-user read entry to the file with
setfacl -m. - Add a named-group read/write entry to the directory.
- Inspect the ACL mask after each modification.
- Create a default ACL on the directory, then create a new file inside it and compare the inherited ACL.
- Remove only the named-user entry with
-x. - Remove the extended ACLs from the disposable file with
-band verify the result.
Knowledge check
- What does
setfacl -mdo? - How do you remove one named-user ACL entry?
- What does the ACL mask limit?
- What is the purpose of a default ACL on a directory?
- What does
setfacl -bremove? - Why is
Xoften safer thanxin recursive ACL changes? - Which command should you use to verify the resulting ACL?
Answer guide
- It modifies or adds ACL entries.
- Use
setfacl -x u:USERNAME FILE. - It caps the effective permissions of named users, the owning group, and named groups.
- It provides ACL entries that newly created children can inherit.
- All extended ACL entries, while retaining the base owner, group, and other entries.
Xadds execute only to directories or files already executable for some user, reducing the chance of making ordinary files executable during a recursive operation.getfacl.
Key takeaway
setfacl is the write side of Linux ACL administration. Use it when ordinary mode bits are too coarse, make the smallest targeted change possible, and verify every result with getfacl—especially the ACL mask and default entries.
References
Primary reference: setfacl(1) — Linux manual page. Related lesson: Linux Command #52 – getfacl.
Advertisement
BitcoinVersus.Tech Editor’s Note:
We volunteer daily to ensure the credibility of the information on this platform is Verifiably True. If you would like to support our independent technical education work, please donate Bitcoin here: 3C9o19EH5HSiwEPyCTmEKzxhNCbo2X6TTb
BitcoinVersus.tech is not a financial advisor. This lesson is for informational and educational purposes.


Leave a Reply