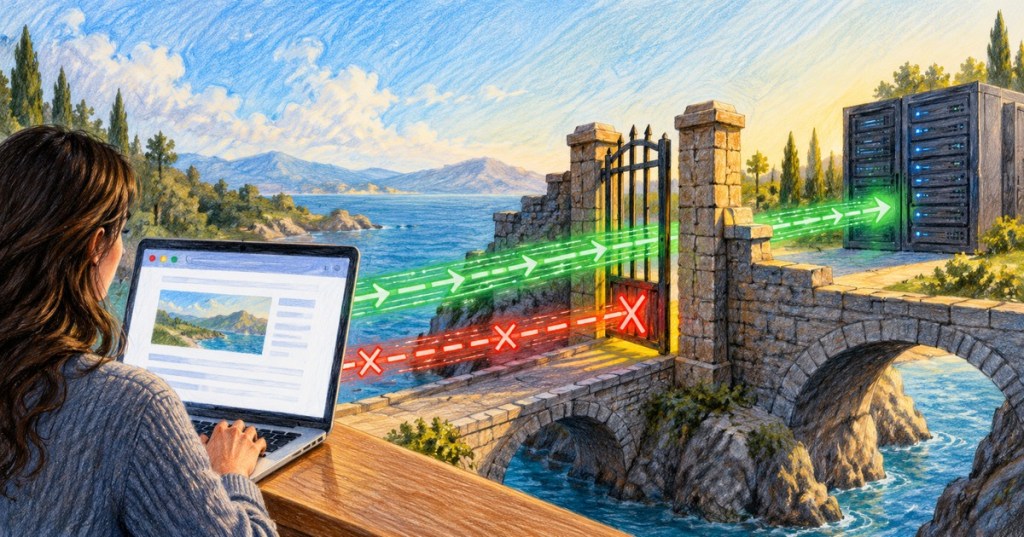
CORS, short for Cross-Origin Resource Sharing, is the browser security system that decides when code on one website is allowed to read a response from another origin. If you have ever seen a browser error mentioning Access-Control-Allow-Origin, CORS is usually the reason.
CORS sounds complicated because several pieces of the web meet at once: browsers, HTTP headers, APIs, cookies, JavaScript, and security policy. The core idea is simpler: the browser asks whether one origin has permission to read data from another.
What Is an Origin?
An origin is defined by three things: the URL scheme, hostname, and port. For example, https://app.example.com and https://api.example.com are different origins because their hostnames differ. Changing from HTTP to HTTPS, or changing the port, can also create a different origin.
This sits on top of ordinary web networking. BitcoinVersus.Tech’s older HTTPS vs HTTP explainer covers the protocol difference, while our JSON explainer covers one of the most common data formats exchanged by web APIs.
Why Browsers Restrict Cross-Origin Requests
Imagine opening a random website and having its JavaScript freely read private responses from your email, banking, cloud-storage, or work applications simply because you were already signed in. Browsers need a boundary between unrelated sites.
The browser’s same-origin policy provides that boundary. CORS is the controlled exception. The MDN CORS guide describes it as an HTTP-header-based mechanism that lets a server identify other origins that a browser may permit to access its resources.
How a Basic CORS Request Works
Suppose JavaScript loaded from https://app.example.com requests data from https://api.example.com. The browser can include an Origin header identifying the requesting origin.
Origin: https://app.example.comIf the API wants that site to read the response, it can return an appropriate CORS response header:
Access-Control-Allow-Origin: https://app.example.comThe server sends the policy. The browser enforces it. If the returned CORS headers do not authorize the requesting origin, browser JavaScript cannot read the response normally.
What Is a Preflight Request?
Some cross-origin requests are more powerful than a basic GET or ordinary form-style request. Before sending them, the browser may first send an HTTP OPTIONS request called a preflight.
The preflight asks questions such as: Is this method allowed? Are these custom headers allowed? Is this origin permitted? The server can answer with headers such as Access-Control-Allow-Methods and Access-Control-Allow-Headers.
The formal WHATWG Fetch Standard defines the CORS protocol, including preflight requests and the headers browsers use to decide whether a response can be shared across origins.
Cookies and Credentials Make CORS Stricter
Cross-origin requests become more sensitive when they include credentials such as cookies or HTTP authentication. A server that allows credentialed cross-origin access must explicitly allow the requesting origin and opt in to credentials with Access-Control-Allow-Credentials: true.
The wildcard * cannot be used as Access-Control-Allow-Origin for a credentialed request. That restriction matters because cookies often carry session state. Our explainer on browser cookies covers how that state works.
CORS Is Not Authentication
A common mistake is treating CORS as if it protects an API by itself. It does not. CORS is mainly a browser-enforced rule about whether frontend code may read a cross-origin response.
Server-side software, command-line tools such as curl, and custom clients are not protected by browser CORS enforcement. An API still needs proper authentication, authorization, input validation, rate limits, and other security controls appropriate to the service.
www hostname.Why CORS Errors Are So Confusing
The browser console may say a request was “blocked by CORS,” but that does not always mean the application server never received a request. In some cases the server processed it and returned a response that the browser refused to expose to JavaScript. In other cases a failed preflight prevents the intended request from being sent.
That difference matters when a request changes data. Repeatedly clicking a button because the browser says “CORS error” can be risky if the server actually completed the operation.
Common CORS Problems
- The server sends no
Access-Control-Allow-Originheader. - The allowed origin does not exactly match the requesting origin.
- An
OPTIONSpreflight is blocked by the application, proxy, firewall, or web server. - The requested method or custom header is missing from the server’s allowlist.
- The application tries to combine credentials with a wildcard origin.
- A reverse proxy or CDN caches the wrong CORS response for another origin.
How to Troubleshoot CORS
- Open the browser developer tools and inspect the Network and Console tabs.
- Confirm the exact requesting origin: scheme, hostname, and port.
- Check whether the browser sent an
OPTIONSpreflight. - Inspect the response headers from both the preflight and actual request.
- Verify that the server allows only the methods, headers, origins, and credentials the application actually needs.
- Test the endpoint separately with a server-side or command-line client so you can distinguish an API failure from browser CORS enforcement.
The Easy Way to Remember It
The same-origin policy says “stay in your own lane.” CORS lets a server open a controlled gate to selected other origins.
When CORS works, browsers can safely support modern web applications whose frontend, API, storage, fonts, or other resources live on different origins. When it fails, the fix usually belongs in the server’s response policy—not in a browser extension that simply turns the protection off.
Editor’s Note
CORS should be configured as narrowly as practical. Do not disable browser security or allow every origin simply to silence an error without understanding which sites need access and whether credentials are involved.
We volunteer daily to improve the credibility of the information on this platform. If you would like to support the research, please donate here: 3C9o19EH5HSiwEPyCTmEKzxhNCbo2X6TTb
BitcoinVersus.tech is not a financial advisor. This media platform reports on technical and financial subjects purely for informational purposes.


Leave a Reply