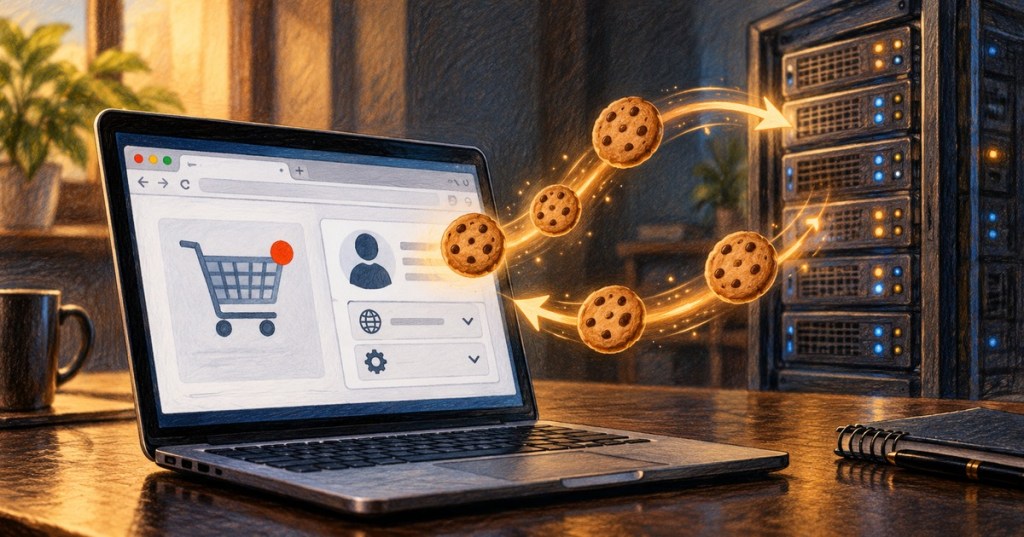
A browser cookie is a small piece of data that a website asks your web browser to store. On a later request, the browser can send that value back to the site. That simple mechanism gives the web something it otherwise lacks: memory between one request and the next.
Cookies are why a shopping cart can still contain your items after you open another page, why a site can remember that you are signed in, and why your preferred language or theme can survive a reload. They can also be used for analytics and advertising, which is why a technology invented to solve a basic web-design problem eventually became one of the most debated pieces of online privacy infrastructure.
The web naturally forgets
When you load a webpage, your browser sends a request to a web server and receives a response. BitcoinVersus covered the larger chain in What Happens When You Type a Website Into Your Browser? The important detail here is that ordinary HTTP requests are fundamentally independent. Without another mechanism, the server does not automatically know that two requests came from the same ongoing session.
That stateless design is useful because it keeps the basic web protocol simple. But it creates an obvious problem for applications. Imagine adding a pair of shoes to a cart, opening the checkout page, and having the store respond as though it had never seen you before. Or imagine entering a password on every page because the site could not remember that you had already authenticated.
Cookies provide a compact answer: the site gives the browser a small identifier or value, the browser stores it under rules set by the site, and later requests can carry it back.
What a cookie actually contains
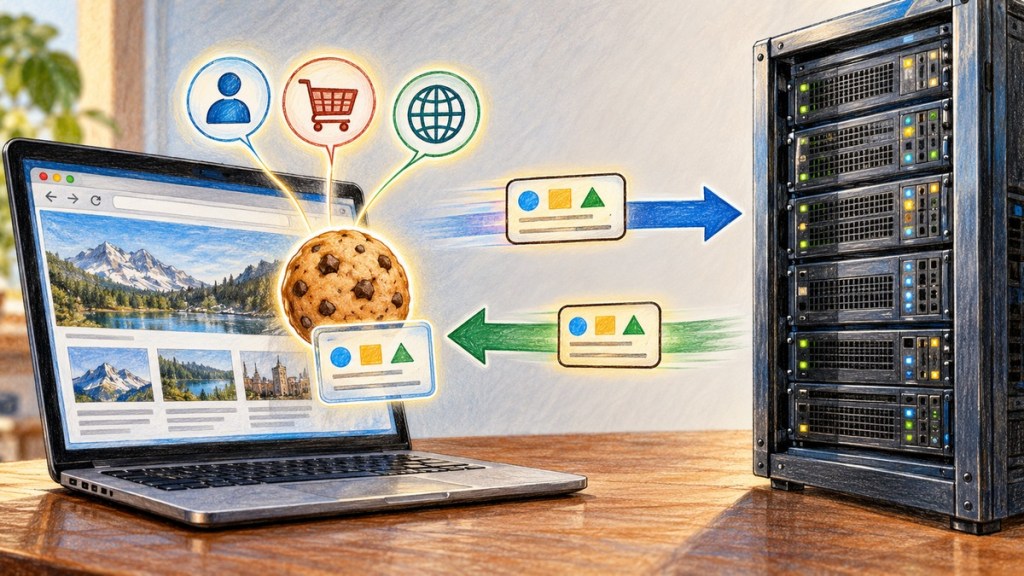
A cookie is not a miniature program running inside your computer. At its simplest, it is a name-and-value pair associated with a website. A server can send one through an HTTP Set-Cookie response header, and the browser can later return eligible cookies in a Cookie request header. MDN’s HTTP cookie guide describes the same request-and-response mechanism.
A site might store a random session identifier such as session=8f31…. The important account information usually stays on the server. When the browser sends that identifier back, the server looks up the corresponding session and knows which signed-in user, cart or preferences belong to that request.
This is why saying “cookies store your password” is usually misleading. Well-designed authentication systems generally use cookies to hold a session token or other limited identifier rather than your actual password. The server-side application—which may communicate with databases and other services through an API—keeps the richer state elsewhere.
Hussein Nasser’s HTTP Cookies Crash Course demonstrates cookie creation, scope, types and security directly at the browser/server level.
The three everyday jobs cookies perform
For most users, cookies matter because they support three broad jobs: session management, personalization and measurement.
- Sessions: keeping you signed in, associating requests with an account, preserving a shopping cart or remembering progress through a multi-step process.
- Personalization: remembering language, region, layout, accessibility choices or other preferences.
- Measurement and tracking: counting visits, measuring campaigns, analyzing behavior or identifying the same browser across repeated interactions.
The first two jobs are why cookies remain useful even on privacy-conscious websites. The third is where the technology becomes controversial, especially when an identifier can follow a browser across many unrelated websites.
First-party and third-party cookies are about context
A “third-party cookie” is not a completely different file format. The distinction comes from context. If you are visiting news.example and that site sets its own cookie, it is acting as the first party. If the page also loads an advertising, analytics or social-media resource from another domain and that outside service can read or set its own cookies inside the page, that service is operating in a third-party context.
That matters because the same advertising or analytics company can appear on thousands of sites. Historically, a shared identifier could make it possible to connect activity across those different sites and build a broader behavioral profile. Cookies did not create online advertising, but third-party cookie access became one of the web’s most important tracking mechanisms.
Firefox has long used tracking protection to restrict cookies and other cross-site tracking mechanisms, illustrating how browser vendors now treat cookie privacy as part of the browser itself.
Browsers now put stronger boundaries around cookies
Modern browsers increasingly separate legitimate website state from cross-site tracking. Firefox’s current Total Cookie Protection isolates cookies into separate site-specific “cookie jars,” making it harder for the same third party to reuse an identifier across unrelated websites. Safari’s cross-site tracking protections similarly restrict third-party access and remove tracking data under defined conditions.
Browser behavior continues to evolve, and different products make different tradeoffs between compatibility, advertising, authentication and privacy. That is why a website that depends heavily on cross-site cookies may behave differently in Safari, Firefox, Chrome or a private-browsing window.
Session cookies versus persistent cookies
Some cookies are intended to last only for a browsing session. Others include an expiration time and can survive browser restarts. A persistent cookie is useful when a site needs to remember a preference or recognize a returning browser days or months later.
“Session cookie” does not necessarily mean the same thing as “login cookie,” and persistent does not automatically mean dangerous. Duration is simply one property. The privacy question depends on what the cookie represents, who can receive it, how long it lasts and how the associated data is used.
Security attributes make cookies safer
Cookies can carry attributes that limit when they are sent or who can access them. You do not need to memorize these to understand the idea, but three are especially important.
- Secure: tells the browser to send the cookie only over encrypted HTTPS connections.
- HttpOnly: prevents ordinary page JavaScript from reading the cookie, which can reduce the damage from some script-injection attacks.
- SameSite: limits when a cookie is included with cross-site requests and helps reduce certain cross-site request attacks.
These protections fit into the broader security model explained in What Is HTTPS? How TLS Certificates Secure the Web. HTTPS protects data while it travels across the network; cookie attributes help define when browser-held state is allowed to travel at all.
What happens when you clear cookies?
Deleting cookies removes the browser-side identifiers and values stored for those sites. That is why clearing cookies can sign you out, empty carts, reset language choices and make a website behave as though you are a new visitor.
It does not necessarily erase every piece of information a company has about you. A website may still have account records, server logs, purchase history or other data stored on its own systems. Cookies are one part of the state relationship between a browser and a service, not the entire data trail.
Cookies are not the same as cache or local storage
A browser cache stores copies of resources such as images, scripts and stylesheets so pages can load faster. Cookies primarily store small pieces of state associated with a site. Other browser storage systems, including local storage and IndexedDB, can hold larger amounts of application data and are not automatically attached to every matching HTTP request.
Modern web applications often use several of these systems together. JavaScript may read or write permitted browser storage, an application may exchange structured JSON data with a server, and cookies may maintain the session that ties those interactions to one user.
Why are there so many cookie banners?
Cookie banners are primarily about data-processing rules and consent, not a technical requirement built into cookies themselves. Privacy laws and regulatory frameworks in different jurisdictions can require websites to disclose certain uses of tracking technologies, provide choices or obtain consent before some non-essential tracking begins.
That is why one site may offer “necessary,” “analytics” and “advertising” categories while another presents a simpler choice. The legal details vary by location and service, but the technical distinction is useful: a cookie needed to keep a shopping cart working is serving a different purpose from a cookie used to build an advertising profile across sites.
Does private browsing eliminate cookies?
No. Private or incognito browsing still needs temporary cookies so websites can function during the session. The main difference is that the browser isolates or discards much of that local state when the private session ends. Private browsing is useful for reducing what remains on your device, but it does not make you invisible to the websites you visit, your network provider or every other party involved in the connection.
Cookies were invented to make shopping carts work
The history helps explain why cookies are not inherently advertising technology. Netscape engineer Lou Montulli developed the web-cookie mechanism in 1994 while working on a way for web commerce systems to maintain state. Montulli later described the basic problem as giving the web a way to remember a user without assigning every browser a universal identifier. Early uses included recognizing repeat visitors and supporting shopping-cart behavior.
The clever part of the design was its modesty: let individual sites store small pieces of state rather than make the entire web remember everyone centrally. The privacy problem grew later as third-party services found ways to use the same mechanism across many sites.
The practical takeaway
You usually do not need to fear every cookie or accept every cookie. The useful question is what the cookie is doing. A session cookie that keeps you signed in is basic web plumbing. A preference cookie may make a site easier to use. A cross-site advertising identifier raises a different privacy question.
- Clearing cookies is useful when a site is stuck, you want to sign out completely, or you want to remove stored site state.
- Blocking every cookie can break logins, carts and other normal website functions.
- Browser privacy controls can restrict cross-site tracking without eliminating the useful first-party state websites depend on.
- Private browsing limits what remains on your device after the session, but it is not an anonymity service.
The best way to think about cookies is not as mysterious files watching everything you do, but as one of the web’s oldest memory mechanisms. They solve a real problem. The ongoing challenge is keeping that memory useful without letting it become a passport for tracking people everywhere they go.


Leave a Reply