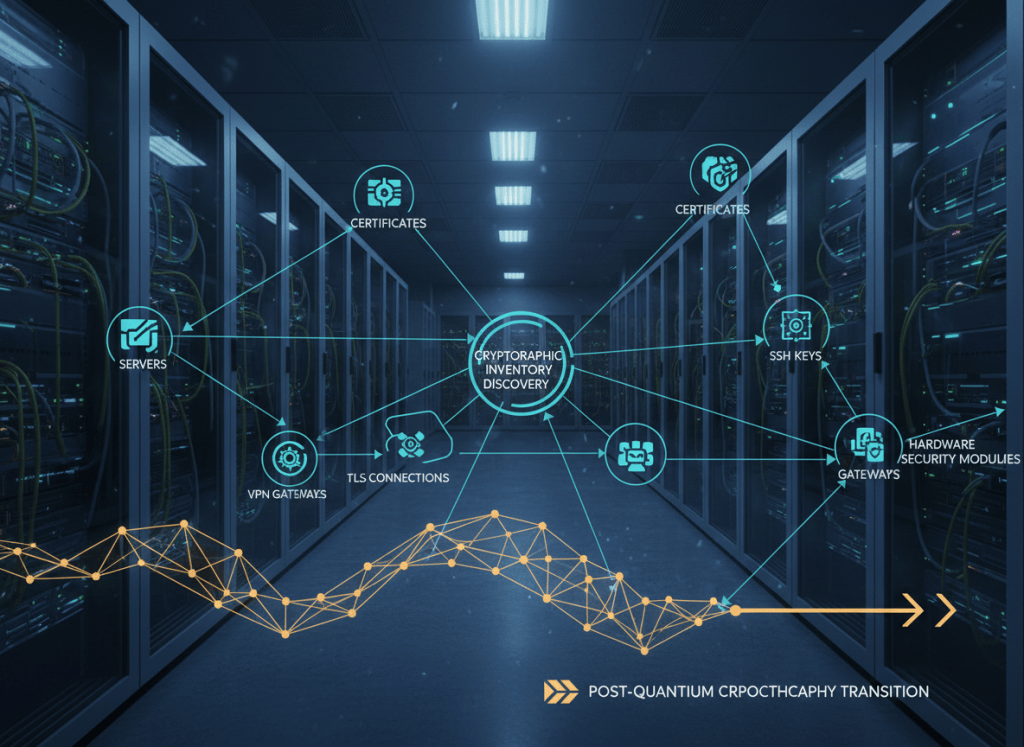
Post-quantum cryptography is often discussed as an algorithm upgrade, but the first practical job for an IT team is more basic: find every place the organization already depends on cryptography.
That means building a cryptographic inventory. The U.S. National Institute of Standards and Technology describes this as a record of cryptography used across systems, applications, services, devices and data flows. A useful inventory can include algorithms such as RSA and elliptic-curve cryptography, protocols such as TLS, SSH and VPNs, certificates and certificate chains, key metadata, cryptographic libraries, hardware security modules and the systems that depend on them. The inventory should track keys without storing the secret key material itself.
Why Discovery Comes Before Migration
NIST finalized its first three post-quantum cryptography standards in 2024 and has encouraged organizations to begin transitioning. But replacing an algorithm safely requires knowing where that algorithm is used. An overlooked certificate, embedded library, VPN appliance, code-signing workflow or legacy service can leave a dependency on cryptography that an organization thought it had retired.
The same principle appears in U.S. federal law. 6 U.S.C. § 1526 requires federal agencies to establish and maintain an inventory of information technology vulnerable to decryption by quantum computers and to prioritize systems for migration. NIST’s National Cybersecurity Center of Excellence likewise places cryptographic visibility and risk management at the center of its migration project.
A Practical Inventory Checklist
Start at the services users and machines actually touch. Record public and internal TLS certificates, SSH services and host keys, VPN gateways, certificate authorities, code-signing systems, encrypted email, application secrets, database encryption, storage encryption and device identity. For each dependency, document the algorithm, key size or parameter set, protocol, software or hardware owner, vendor, expiration or lifecycle date, data sensitivity and the system that will break if the cryptography changes.
Then classify the inventory by risk. Long-lived sensitive information deserves special attention because encrypted data captured today could potentially be retained for later decryption if sufficiently capable quantum computers become available. Internet-facing services, identity infrastructure and systems that cannot be upgraded quickly also deserve early testing.
This is related to security fundamentals BitcoinVersus.tech has covered in Kerberos: Network Authenticator and Information Security: Confidentiality, Integrity, and Availability. Quantum migration adds a new constraint, but the operational discipline is familiar: know the asset, know the dependency, know the owner and test the replacement before production.
QShield 2.0 Puts Discovery Into a Commercial Platform
On September 19, 2026, Bengaluru-based QNu Labs announced QShield 2.0, which powers the company’s National Cryptographic Assessment & Assurance Framework. QNu describes the framework as a continuous cycle of Discover, Assess and Assure: locate cryptographic assets, evaluate classical and quantum risk, then keep checking as systems and standards change.
QNu says the platform combines five modules covering quantum entropy, quantum-readiness risk assessment, quantum PKI, a cryptographic vault and AI security. Those product claims should be evaluated independently for a specific deployment, but the architecture highlights an important industry direction: cryptographic discovery is becoming a managed operational function rather than a one-time spreadsheet exercise.
The Goal Is Crypto Agility
A complete inventory is not the finish line. It is the map that makes crypto agility possible: the ability to replace cryptographic algorithms or implementations without rebuilding an entire application stack. Organizations should test post-quantum replacements in controlled environments, measure interoperability and performance, verify vendor support, and maintain rollback plans before changing production trust infrastructure.
The simplest technical lesson is also the most useful: you cannot migrate cryptography you cannot find. Before an organization debates which post-quantum algorithm belongs in every system, it should be able to answer where its cryptography lives today.
BitcoinVersus.Tech Editor’s Note:
We volunteer daily to ensure the credibility of the information on this platform is Verifiably True. If you would like to support to help further secure the integrity of our research initiatives, please donate here: 3C9o19EH5HSiwEPyCTmEKzxhNCbo2X6TTb
https://x.com/1BitcoinVersus/status/1937006164555993338
BitcoinVersus.tech is not a financial advisor. This media platform reports on financial subjects purely for informational purposes.
 Bitcoin Versus

Leave a comment