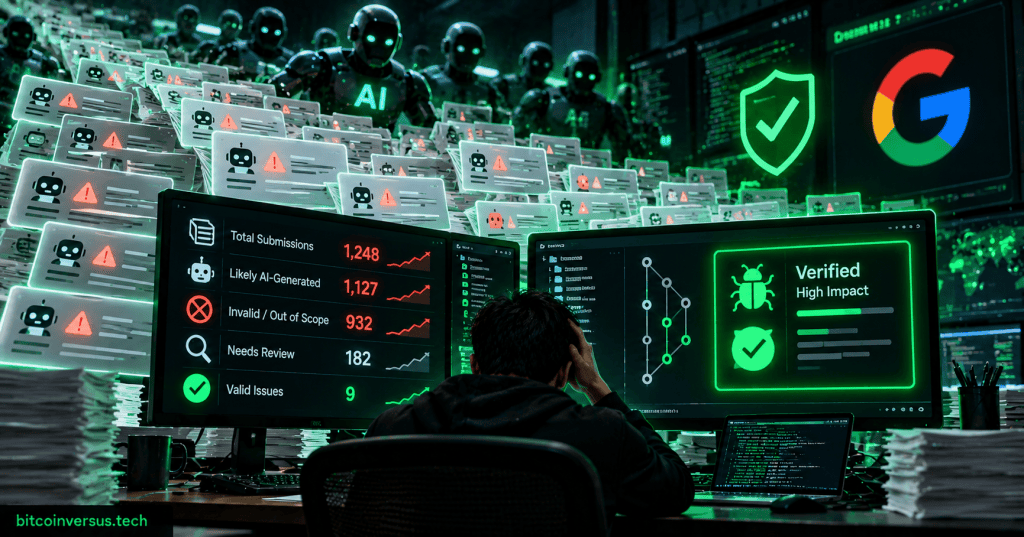
Google has temporarily stopped accepting new product-vulnerability submissions to its Open Source Software Vulnerability Reward Program after automated reports flooded the intake pipeline. The company says the vast majority of those new automated submissions were not valid, turning AI-assisted security research into a triage problem for the humans maintaining the program.
The current Google Bug Hunters OSS VRP rules remain the primary program reference, while TechCrunch’s October 4 report confirms that new product-vulnerability submissions were paused beginning October 1 and that Google expects to provide an update in the first quarter of 2027.
Google did not shut down every bug bounty
The scope of the pause is narrower than a full bug-bounty shutdown. Google says outstanding reports already in the system are not affected, and OSS VRP supply-chain reports can still be submitted. Researchers are also being directed toward Google’s other vulnerability-reward programs and its Patch Rewards Program.
That distinction matters because bug-bounty programs are part of the defensive layer that helps major software projects surface flaws before attackers do. BitcoinVersus.Tech recently covered Vercel’s KVM zero-day VM escape, a reminder that serious infrastructure vulnerabilities still require fast, technically grounded reporting rather than volume for its own sake.
Google announced the change directly in its Google VRP post on X, saying the pause was caused by a significant rise in automated submissions and that the vast majority were invalid.
AI can find bugs faster — and manufacture noise faster
The problem is not that AI-assisted vulnerability research is useless. The same tools that help developers inspect code can help researchers identify suspicious patterns, generate test cases and automate repetitive analysis. The failure mode appears when a model’s output is treated as a finished security finding instead of a hypothesis that still needs proof.
A model can point at a buffer overflow, suspicious permission check or potentially dangerous code path while missing the fact that the code is unreachable, already sandboxed or impossible to trigger under the product’s real security model. If thousands of those reports are automatically submitted, human triagers spend time disproving machine-generated claims instead of validating the small number of issues that actually matter.
The bottleneck moved from bug discovery to bug validation
That is the broader signal from Google’s pause. AI is making it cheaper to generate candidate vulnerabilities, but verification remains expensive. Reproducing an issue, demonstrating real impact, proving an exploit path and understanding whether a security boundary is actually crossed still require disciplined engineering work.
The same asymmetry appears elsewhere in AI security. BitcoinVersus.Tech recently examined Apple tightening macOS Full Disk Access as AI agents create new privacy risks. Giving software more autonomy can increase useful output, but it also creates more states, permissions and failure modes that must be validated rather than assumed safe.
Open-source maintainers are especially exposed to AI-generated report spam
Large companies can dedicate teams to security intake. Smaller open-source projects often cannot. A maintainer may already be balancing feature work, bug fixes, pull requests and user support without a full-time security team. A wave of plausible-looking but invalid vulnerability reports can therefore consume the same limited attention needed to fix genuine issues.
This creates an uncomfortable security paradox: automation can increase the number of potential bugs discovered while making it harder for maintainers to identify the ones worth acting on. The value of the system depends increasingly on validation quality, not report count.
Security programs may start demanding machine-verifiable proof
The likely response is stricter evidence. Security programs can require reproducible test cases, working proof-of-concept code, deterministic fuzzing output, merged patches or other artifacts that make a report cheaper to validate. AI can still help create those artifacts, but the submission has to survive an objective check before it reaches a human reviewer.
That approach also reduces the advantage of simply generating more reports. If every submission must demonstrate an actual security boundary violation, the model is forced closer to the same standard a skilled human researcher would be expected to meet.
BitcoinVersus.Tech’s recent report on the ShinyHunters investigation illustrates the other side of the equation: real security incidents still demand high-confidence attribution, evidence and investigative work. Automated volume cannot replace proof.
Google’s pause is an early warning for every bug-bounty operator
The important lesson is not that AI should be banned from security research. It is that AI makes quality control more important because the cost of producing convincing-looking technical text has collapsed.
If Google’s program redesign succeeds, the next generation of bug bounties may treat automated discovery as normal while placing much more weight on verified impact. That would move the incentive away from submitting the most reports and toward proving the few vulnerabilities that actually cross a security boundary.
BitcoinVersus.Tech
Advertisement
Editor’s Note
If you value independent technology reporting, consider supporting BitcoinVersus.Tech with a Bitcoin donation: 3C9o19EH5HSiwEPyCTmEKzxhNCbo2X6TTb
BitcoinVersus.tech is not a financial advisor. This media platform reports on financial subjects purely for informational purposes.


Leave a comment