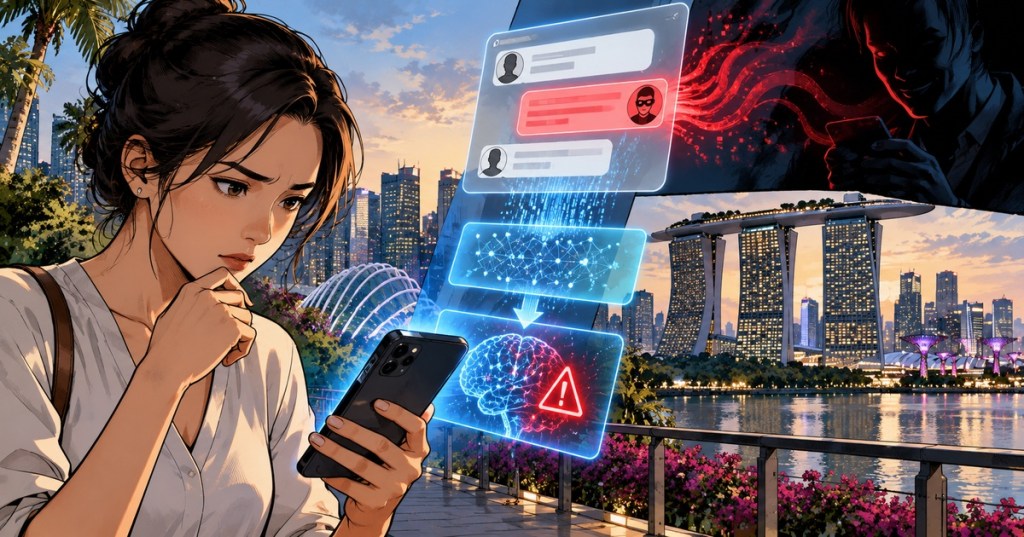
Singapore is testing a new way to fight conversational scams without sending private chats to a cloud server. On October 14, 2026, Google DeepMind and Singapore’s Government Technology Agency announced an on-device scam detection model built to recognize manipulative patterns inside multi-turn conversations while keeping message analysis on the user’s phone.
The project targets a difficult part of modern fraud: scams that do not look obviously malicious in a single message. Instead, an attacker may spend minutes or days building trust, impersonating a bank, government agency, executive or public figure before asking for credentials or money. Google DeepMind says these social-engineering conversations now account for up to 80% of scam losses in Singapore, while scams overall have caused more than S$4 billion in losses since 2019.
The technical design is a two-stage pipeline. The first stage is a lightweight classifier that screens inbound messages using relatively little power. Conversations that appear benign can stop there. Suspicious activity is passed to a second stage: a fine-tuned Gemma model that examines a broader window of the conversation to decide whether manipulation is occurring. If the model identifies a likely scam, it can trigger an immediate warning telling the user to pause before sending money or sensitive information.
Google for Developers demonstrates Gemma 3n, a mobile-first model family designed for efficient multimodal AI running directly on everyday devices.
Why On-Device Detection Matters
The most important architectural choice is where that second-stage analysis happens. Google DeepMind says the conversation snapshot is processed on-device rather than uploaded to a remote server. That matters because many messaging services use end-to-end encryption. Server-side scanning can conflict with the privacy model of those services, while local inference can analyze content after it reaches the authorized user’s device without requiring the service provider to read the messages in the cloud.
This does not mean privacy questions disappear. An on-device model still needs permissions, memory, compute and a secure application boundary, and developers need clear rules about what conversation context is retained. But keeping inference local can reduce the amount of sensitive data transmitted to external infrastructure. BitcoinVersus.Tech recently ranked AI assistants for privacy, and the same principle appears here: where computation occurs can be just as important as what the model can do.
Google DeepMind says the model was fine-tuned on localized scam conversations covering impersonations of public institutions, banks and local figures as well as regional scam patterns. The goal is important because a generic fraud classifier trained primarily on another country’s language, institutions and scam habits may miss the cues Singapore users actually see. Local fine-tuning is one way to make a smaller model more useful without making it universally large.
That approach also fits the larger move toward edge AI. BitcoinVersus.Tech previously covered Singapore’s HELIX Lab and its push toward edge AI hardware using 18nm FD-SOI and phase-change memory. The scam-detection project tackles a different layer of the stack, but the direction is similar: move useful intelligence closer to the device so latency, privacy and connectivity constraints become easier to manage.
Google for Developers explains the broader Google AI Edge stack for running AI locally with lower latency, offline capability and greater control over private data.
Singapore Confirms the Project
Singapore’s Ministry of Digital Development and Information independently confirmed the collaboration during Singapore International Cyber Week. Minister Josephine Teo said GovTech is working with Google DeepMind to develop real-time AI detection of scams on devices so signs of manipulation can be recognized early while personal messages remain on the device. The project was presented at SICW 2026.
The government context helps explain why Singapore is investing heavily here. GovTech says scams represented more than half of reported crimes, and the agency’s current anti-scam stack already combines mobile tools, automated website analysis and law-enforcement workflows. ScamShield, for example, can check suspicious calls, links and messages, while GovTech says the suite has blocked or blacklisted more than 120,000 scam entities since 2022 and has been downloaded more than 900,000 times.
GovTech Singapore has publicly documented its broader AI-driven anti-scam work, including systems designed to detect malicious websites and other scam infrastructure.
A second system, SATIS, operates farther upstream. GovTech says SATIS and its recursive Machine-Learning Site Evaluator continuously review more than 400,000 websites per day, with over 90% accuracy and less than 0.1% false positives after human-machine verification. The agency says the system disrupts more than 15,000 malicious websites in an average month. Those figures are government-reported performance measures, but they show that Singapore is not starting from zero: the new DeepMind model would join an existing multi-layer anti-scam system rather than replace it.
The Gap Website Scanners Cannot See
The conversational model addresses a gap website scanning cannot solve. A scammer can use a legitimate messaging platform, a normal-looking account and no malicious link at all. The fraud may depend entirely on persuasion: “I am your boss,” “I am from the police,” “your account is at risk,” or “move the money now.” A URL classifier cannot reliably detect that kind of social pressure because the dangerous signal may be spread across several ordinary-looking sentences.
That is why multi-turn context matters. A single request to “confirm your name” can be harmless. A later request to install an app, disclose a one-time password or transfer funds can change the meaning of the earlier exchange. An on-device language model can potentially evaluate that sequence as a pattern instead of treating every message independently.
Google for Developers shows how newer Gemma models run inside the AI Edge Gallery, illustrating how increasingly capable language models are moving onto local hardware.
What Is Not Proven Yet
There are still limitations. Google DeepMind has not published a full public benchmark showing detection rates across every scam category, device class and language used in Singapore. The announcement also does not mean every WhatsApp, Telegram, iMessage or SMS conversation in Singapore is now automatically protected by this model. DeepMind explicitly says messaging platforms and operating-system vendors can integrate lightweight models like this. Deployment therefore depends on product integration, permissions, user experience and platform policy.
False positives will matter too. A security model that warns too often can train users to ignore it. A model that is too cautious can miss sophisticated fraud. Localized models must also keep up with scam tactics that change quickly. Scammers can alter vocabulary, pacing, impersonated institutions and requested actions once they understand how detection systems behave.
The training process was designed with governance controls. DeepMind says fine-tuning occurred inside GovTech’s managed Google Cloud environment, with training data isolated in what it describes as a sovereign sandbox. It says private citizen data and personally identifiable information were excluded, with training instead based on anonymized material derived from scam reports and intelligence feeds. The system was also stress-tested with synthetic dialogues and local corpora.
That governance model is notable because anti-fraud AI can create a temptation to collect more private information in the name of safety. The Singapore project is trying to take the opposite route: use local inference and controlled training data to reduce how much personal conversation data leaves the device. It is not proof that every privacy risk has been solved, but it is a concrete engineering choice rather than a policy slogan.
Scam technology has already shown why this tradeoff matters. BitcoinVersus.Tech previously reported how a phishing email targeting Trezor users came from its real domain, demonstrating that familiar trust signals can be compromised. As attackers gain access to better generative AI, voice synthesis and deepfake tools, users will increasingly face messages that look polished, personalized and context-aware. Detection systems will need to judge behavior, not just spelling mistakes or suspicious URLs.
Why This Could Matter Beyond Singapore
Singapore’s latest approach is therefore worth watching beyond Singapore. If a relatively small model can run efficiently on mainstream phones, detect manipulation across several messages and keep the content local, the same architecture could be adapted to banking apps, messaging platforms, enterprise chat systems or telecom anti-fraud tools in other countries.
The larger lesson is that some of the most practical AI deployments may not require a giant cloud model answering open-ended questions. A smaller model trained for one high-value task, running privately on hardware people already own, can be more useful. In this case, the task is simple to describe but difficult to execute: recognize when a conversation is turning into a scam before the user sends the money.
BitcoinVersus.Tech Editor’s Note:
We volunteer daily to ensure the credibility of the information on this platform is Verifiably True. If you would like to support to help further secure the integrity of our research initiatives, please donate using the QR code provided

For best QR-code scanning results, please scan this donation code from a desktop or larger screen. Mobile screens may prevent camera recognition.


Leave a Reply