Elementary Overview
On Linux, a user password can have a schedule as well as a value. The chage command manages that schedule: when a password was last changed, how long it may be used, how early the user is warned, how long an expired password may remain inactive, and when the account itself expires. It works alongside passwd, which changes or expires passwords, and the account-management commands useradd, usermod, and userdel. The simplest mental model is that passwd manages the password itself, while chage manages the password’s calendar.
Read the Current Aging Policy With chage -l
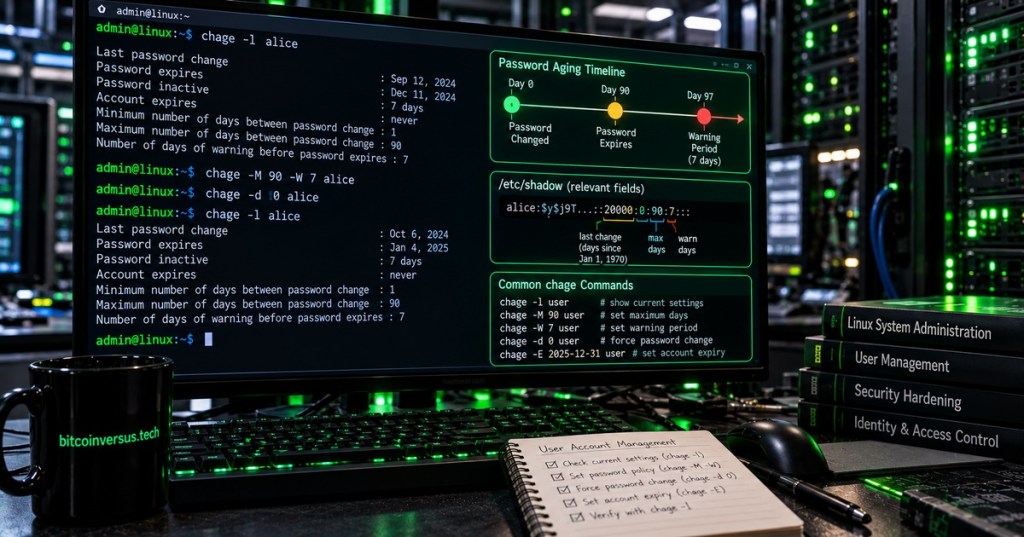
The safest first step is inspection. sudo chage -l alice lists the account’s current password-aging values in human-readable form: last password change, password expiration date, inactive period, account expiration date, minimum days between changes, maximum days before expiration, and warning days. That makes chage -l a useful companion to getent when auditing local account state. Reading before writing is especially important on production systems because an aggressive aging change can force an unexpected password reset or make an account unavailable at the next login.
Set Minimum, Maximum, Warning, and Inactive Periods
The main policy switches correspond to stages on a password-aging timeline. sudo chage -m 1 alice sets a minimum of one day before another password change is allowed; sudo chage -M 90 alice sets a 90-day maximum age; sudo chage -W 7 alice warns the user seven days before expiration; and sudo chage -I 14 alice allows fourteen inactive days after password expiration before the account becomes unavailable. These values should come from the organization’s real authentication policy rather than arbitrary numbers. The command provides the mechanism; security policy determines the correct settings.
Force a Password Change or Set an Account Expiration Date
sudo chage -d 0 alice sets the last-password-change value so the user must choose a new password at the next applicable login. This is useful for temporary passwords created during account provisioning, and it overlaps conceptually with the expiration behavior available through passwd. A separate control, sudo chage -E 2026-12-31 alice, sets an expiration date for the account itself. Password expiration and account expiration are different: one says the credential is too old, while the other says the account has reached the end of its permitted lifetime.
chage Works Through /etc/shadow, Not Through a Separate Password Database
Password-aging metadata for local Linux accounts is stored in /etc/shadow. Fields represent the last password change as a day count, minimum and maximum ages, warning period, inactivity period, and account expiration. chage gives administrators a safer human-readable interface to those values instead of manually editing the protected file. Defaults for newly created local accounts can also be influenced by configuration such as /etc/login.defs, while authentication frameworks such as PAM may enforce additional password-quality or login policy. This separation is why changing one chage value does not automatically define every aspect of Linux authentication security.
Practical Command Set
sudo chage -l alice— list the current aging policy.sudo chage -m 1 alice— minimum one day between password changes.sudo chage -M 90 alice— maximum password age of 90 days.sudo chage -W 7 alice— warn seven days before expiration.sudo chage -I 14 alice— make the account inactive 14 days after password expiration.sudo chage -d 0 alice— require a password change at the next applicable login.sudo chage -E 2026-12-31 alice— expire the account on a specific date.sudo chage alice— open interactive mode for several aging fields.
Exercises
- Create or select a lab-only user and inspect its policy with
chage -l. - Set a 60-day maximum password age and a 10-day warning period, then verify both values.
- Explain the difference between
-M,-I, and-E. - Force a password change on the next login in a disposable lab account, then inspect the resulting aging data.
- Compare the account information visible through
getent passwd USERwith the policy information visible throughchage -l USER. - Explain why manually editing
/etc/shadowis normally less desirable than using an account-management command.
Knowledge Check + Answers
- What does
chage -ldo? It lists the password-aging and account-expiration information for a user. - What does
-Mcontrol? The maximum number of days a password may be used before expiration. - What does
-Wcontrol? The number of warning days before password expiration. - What does
-d 0commonly accomplish? It forces the password to be changed at the next applicable login. - What does
-Econtrol? The account expiration date. - Where is local password-aging metadata stored? In
/etc/shadow.
Elementary Conclusion
chage is basically a calendar manager for a Linux user account. The password is still the secret used to prove identity, but chage can say how long that secret is allowed to remain valid, when the user should be warned, how long an expired password may remain inactive, and when the entire account should stop working. A careful administrator first reads the current policy, changes only the required field, and reads it again to verify the result. Together with user creation, account modification, password management, and account removal, it completes an important part of the Linux user-account lifecycle.
BitcoinVersus.Tech
Advertisement
Editor’s Note:
We volunteer daily to ensure the credibility of the information on this platform is Verifiably True. If you would like to support our research initiatives, please donate here: 3C9o19EH5HSiwEPyCTmEKzxhNCbo2X6TTb
BitcoinVersus.tech is not a financial advisor. This media platform reports on financial subjects purely for informational purposes.


Leave a comment