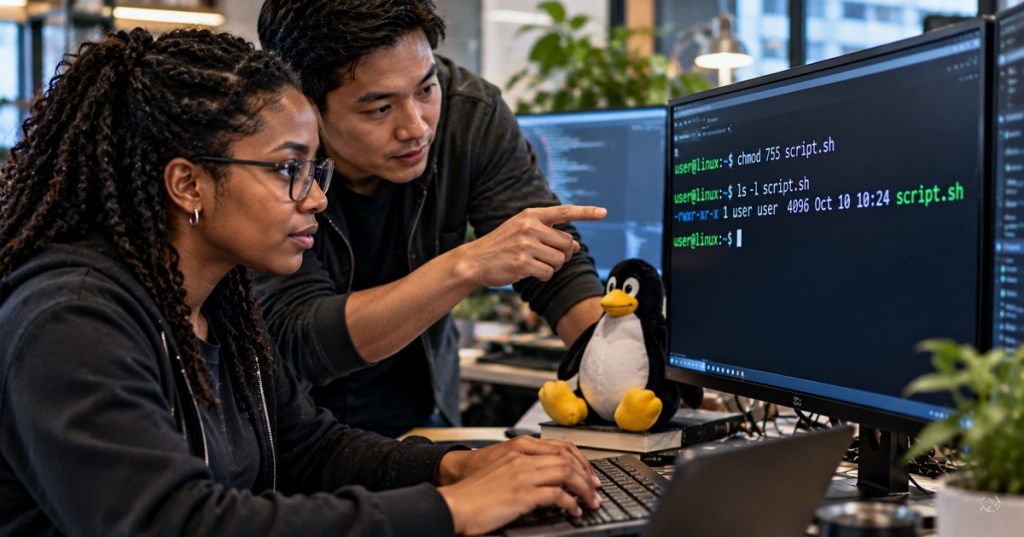
The chmod command changes who can read, write, or execute a file in Linux. It is the natural follow-up to Linux Command #49 – chown, which changes ownership. Ownership and permissions work together, but they are different controls.
What chmod means
chmod means change mode. It changes file permission bits for the owner (u), group (g), others (o), or everyone (a). Permissions are read (r), write (w), and execute (x). For directories, execute means permission to traverse or search the directory.
Syntax and examples
The basic syntax is chmod MODE FILE. Run ls -l filename before and after changing permissions.
chmod u+x script.sh— give the owner execute permission.chmod g-w report.txt— remove group write permission.chmod 644 report.txt— owner can read and write; group and others can read.chmod 755 script.sh— owner can read, write and execute; group and others can read and execute.chmod 600 secrets.txt— owner can read and write; group and others have no permissions.
Understanding numeric modes
Numeric permissions add read = 4, write = 2, and execute = 1. Each digit applies to the owner, group, or others. Thus 7 = 4+2+1, 6 = 4+2, and 5 = 4+1. A mode of 755 is rwxr-xr-x for a regular file.
Changing directories safely
Be cautious with recursive permissions. chmod -R changes every item below a directory, potentially affecting files that should not be executable or writable. For a directory tree that needs access without making every ordinary file executable, GNU chmod supports chmod -R u+rwX directory/: uppercase X adds execute/search only to directories and files that already have execute permission for someone.
Never run an unreviewed recursive chmod against system directories or use chmod -R 777 as a quick fix. World-writable permissions can expose sensitive data and undermine service security. File access can also depend on ACLs and other system controls.
Guided lab
- In a disposable practice folder, create a file with
touch demo.sh. - Check its current permissions with
ls -l demo.sh. - Run
chmod u+x demo.shand inspect the permissions again. - Run
chmod 644 demo.shand confirm the execute bits are gone. - Run
chmod 600 demo.shand explain who can read the file.
Knowledge check and answers
1. What does chmod change? File mode or permission bits, not the file owner. 2. What does 7 represent? Read, write, and execute (4+2+1). 3. Why is uppercase X useful? It can grant directory traversal without indiscriminately making ordinary files executable. 4. Which command changes ownership instead? chown.
Further learning
Read the GNU Coreutils chmod manual and Linux chmod(1) manual page for symbolic and octal modes, recursion, and special permission bits. Review the preceding chown lesson and chgrp lesson to understand how owner, group, and permission settings fit together.


Leave a Reply