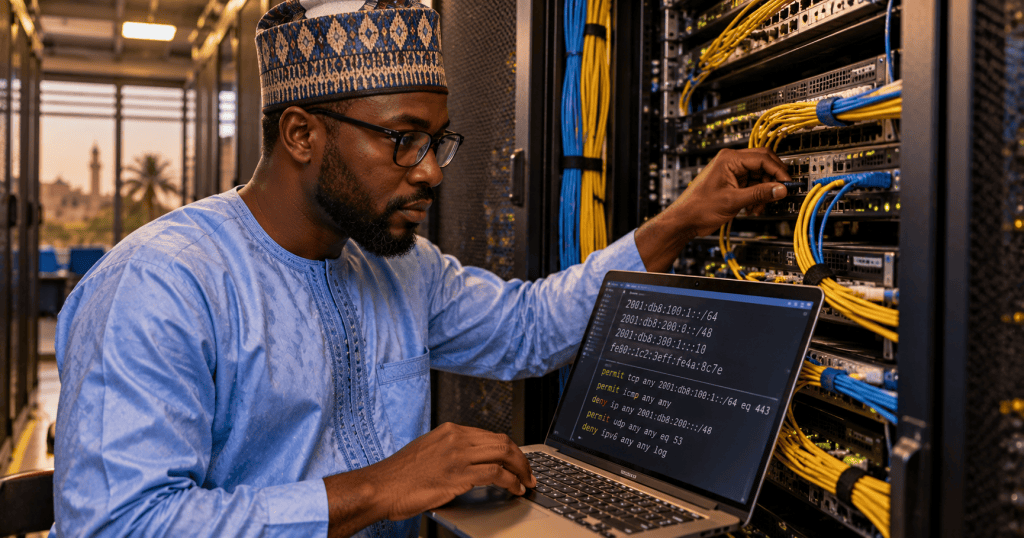
IPv6 access control lists (ACLs) filter traffic using IPv6 source and destination prefixes, protocols, and transport-layer ports. This lesson builds on OSNTC.028: IPv4 Access Control Lists. It emphasizes how IPv6 filtering differs from IPv4 and how to avoid accidentally disrupting basic network operation.
Learning objectives
- Recognize IPv6 prefix notation and named ACL syntax.
- Apply an IPv6 ACL in the intended interface direction.
- Explain first-match processing and the implicit deny.
- Identify essential ICMPv6 functions.
- Validate security controls without confusing stateless ACLs with stateful firewalls.
IPv6 prefixes and traffic matches
An IPv6 address has 128 bits. A prefix such as 2001:db8:10::/64 matches the first 64 bits; the documentation prefix 2001:db8::/32 is reserved for examples and should not be deployed as real public addressing. IPv6 ACLs typically match source and destination prefixes directly rather than using IPv4 wildcard masks.
Named ACLs and ordered rules
On supported Cisco IOS platforms, create a named IPv6 ACL using ipv6 access-list LAB-V6. Add specific permit or deny entries for the intended flows. An illustrative rule is permit tcp 2001:db8:10::/64 host 2001:db8:20::10 eq 443. Syntax and available keywords vary by device family and software version; consult the target platform documentation.
ACLs generally evaluate entries in order and stop at the first match. Most have an implicit deny at the end, so a narrow permit without additional provisions can unintentionally block legitimate traffic. Some IPv6 ACL implementations include implicit Neighbor Discovery-related permits; behavior must be checked against the actual platform and ACL type.
Practical Networking demonstrates IPv6 ACL syntax, matching, sequence ordering, and configuration.
Applying the ACL
On Cisco IOS interfaces that support this syntax, ipv6 traffic-filter LAB-V6 in applies the named ACL to incoming IPv6 packets on that interface. The word in describes the direction relative to the interface, not a blanket inbound-from-the-internet rule. Trace the actual packet path before deployment.
Practical Networking shows how IPv4 and IPv6 ACLs attach to interfaces and why direction matters.
ICMPv6 is not optional noise
IPv6 depends on ICMPv6 for essential functions, including Neighbor Discovery and Path MTU Discovery. Blanket blocking can break neighbor resolution, router discovery, and delivery of packets across links with different maximum transmission units. Design explicit policy that preserves necessary ICMPv6 types and codes for the applicable security zone. Do not blindly allow all ICMPv6 from untrusted sources either; evaluate the environment.
ACLs versus stateful firewalls
A traditional router ACL is typically stateless: permitting outbound traffic does not automatically permit every corresponding return packet. Stateful firewalls track connections and can enforce return-traffic policy differently. Both have legitimate roles, but neither should be confused with address translation. IPv6 generally does not require NAT for ordinary end-to-end addressing.
Network operators discuss where stateless ACLs are appropriate and when stateful inspection is preferable.
Dual-stack risks
In dual-stack networks, an IPv4 security policy does not automatically protect IPv6. Endpoints may use IPv6 link-local connectivity within a VLAN even when no global IPv6 routing is configured. Inventory both protocols and test endpoint, switch, and firewall behavior.
Administrators discuss the difference between disabling routed IPv6 and controlling local IPv6 communications.
Verification workflow
- Record the intended source, destination, protocol, port, interface, and direction.
- Back up the current configuration and establish an approved rollback path.
- Apply the minimum policy in a test environment before production.
- Inspect
show ipv6 access-listand the interface configuration, using the commands supported by your platform. - Test permitted and denied traffic separately, including ICMPv6 and return paths.
- Check counters and logs, while remembering that hardware offload may affect visibility.
- Verify IPv4 and IPv6 behavior independently on dual-stack hosts.
Practice exercise
A lab contains clients on 2001:db8:10::/64 and a server at 2001:db8:20::10. Draft a policy allowing TCP 443 from the client prefix to that server while blocking other unwanted inter-subnet application traffic. Document the ICMPv6 exceptions required by your device and topology. Apply the policy in the correct direction and prove both successful and blocked test cases.
Knowledge check and answers
- What does /64 mean? The first 64 address bits identify the prefix.
- Do IPv6 ACLs use IPv4 wildcard masks? Typically no; they use IPv6 prefixes.
- What does an interface inbound ACL inspect? Packets entering that interface.
- Why avoid a blanket ICMPv6 deny? It can break Neighbor Discovery and Path MTU Discovery.
- Does an ACL automatically track return sessions? A conventional stateless ACL does not.
Primary documentation
Review RFC 4443 (ICMPv6), RFC 4861 (Neighbor Discovery), and RFC 8200 (IPv6 Specification). For implementation, use your switch or router vendor’s ACL documentation for the exact hardware and software version.
Related lessons
BitcoinVersus.Tech Editor’s Note:
We volunteer daily to ensure the credibility of the information on this platform is Verifiably True. If you would like to support to help further secure the integrity of our research initiatives, please donate using the QR code provided
For best QR-code scanning results, please scan this donation code from a desktop or larger screen. Mobile screens may prevent camera recognition.



Leave a Reply