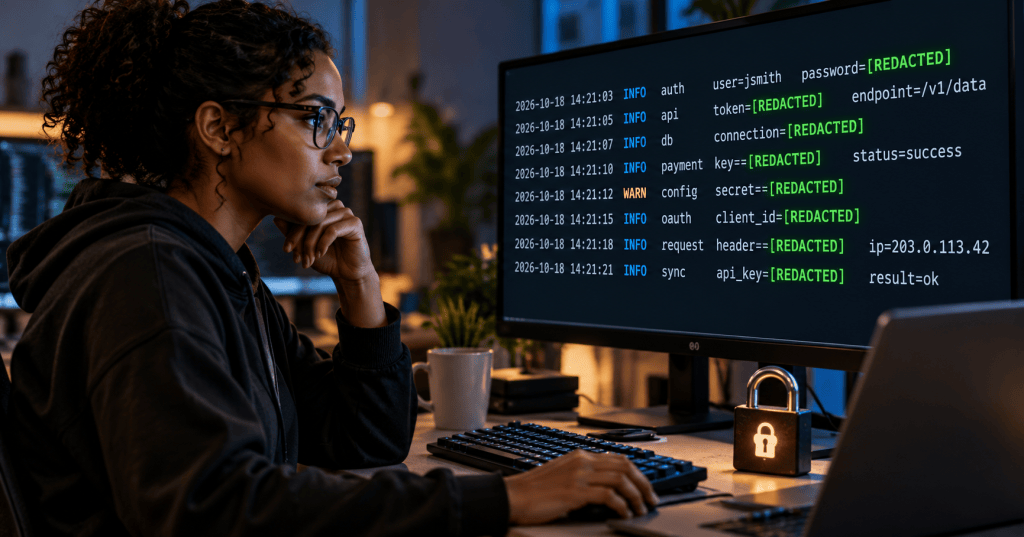
This lesson introduces a focused Python logging skill: preventing passwords, access tokens and other secrets from appearing in application logs. It follows OSPython.040 on asyncio logging.
Learning Objectives
Explain why logs can expose sensitive data; implement a logging filter for known secret fields; test both ordinary and exception logging; understand why application-level redaction is only one layer of protection.
Why Logs Need Protection
Logs are copied to files, monitoring services and support tickets. Recording a password or API key can expose that credential to people and systems that should not have access. The safest approach is to avoid putting secrets into log messages at all.
A Minimal Redaction Filter
Example command:
import logging class SecretFilter(logging.Filter): def filter(self, record): message = record.getMessage() for secret in ("example-token-123",): message = message.replace(secret, "[REDACTED]") record.msg = message record.args = () return True handler = logging.StreamHandler() handler.addFilter(SecretFilter()) logging.basicConfig(level=logging.INFO, handlers=[handler]) logging.info("Token: %s", "example-token-123")
The example prints Token: [REDACTED]. It illustrates how a handler filter can transform a log record before output. It is not a complete production solution: hardcoding a list of secrets is difficult to maintain, structured logging fields may need separate handling, and exceptions or other handlers can expose values through different paths.
Prefer Safe Logging at the Source
Example command:
import logging logging.basicConfig(level=logging.INFO) username = "alice" # Record an event without logging the password or token. logging.info("Authentication attempted for user %s", username)
A stronger policy is to log the event and safe context, but never the credential. Restrict access to logs, establish retention limits and test error paths. If a credential is accidentally recorded, treat it as exposed and follow the appropriate incident response and credential-rotation process.
Knowledge Check
1. Why is logging a token risky? 2. What does a logging filter receive? 3. Why is source-level omission preferable to replacing known strings? 4. Can another handler still expose a secret if it lacks the filter?
Answers
1. Logs may be distributed or retained. 2. A LogRecord. 3. It avoids creating sensitive log content in the first place. 4. Yes.
Community Discussion: Logging Sensitive Information
Python developers discuss why preventing sensitive values from entering logs is safer than relying on cleanup after collection. Read the original community discussion above.
References
Python logging documentation; Python Logging Cookbook; OWASP Logging Cheat Sheet.
BitcoinVersus.Tech Editor’s Note: We volunteer daily to ensure the credibility of the information on this platform is Verifiably True. If you would like to support to help further secure the integrity of our research initiatives, please donate using the QR code provided
For best QR-code scanning results, please scan this donation code from a desktop or larger screen. Mobile screens may prevent camera recognition.


Leave a Reply