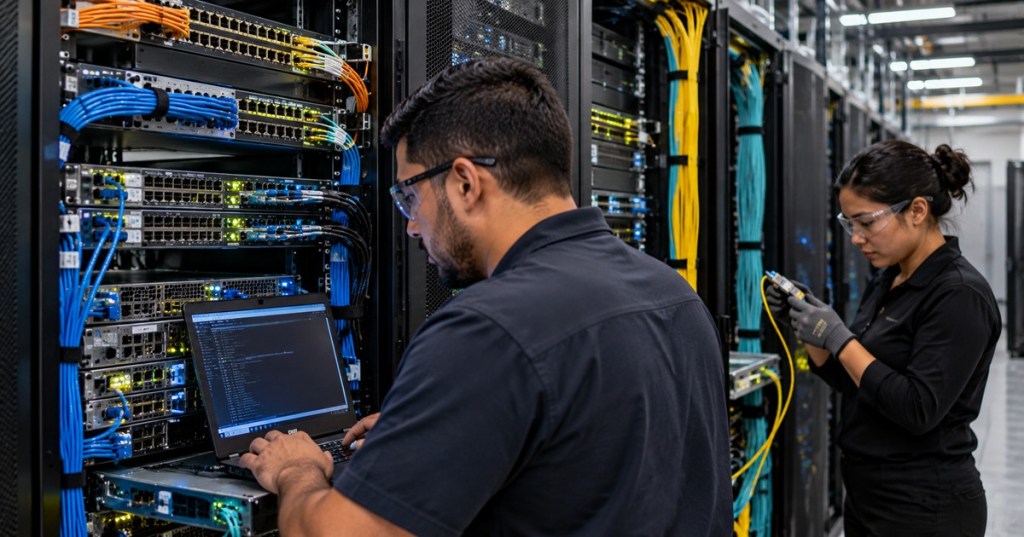
Elementary Overview
A server is not ready for production just because the operating system installed successfully. The network path must also be proven from the physical NIC through cabling and optics, the top-of-rack switch, VLAN or bond configuration, IP settings, routing, and the application-facing network.
This lesson follows OSDCTC.007: Server Provisioning and Deployment. Provisioning creates the host. Network configuration and validation proves that the host is attached to the correct production network with the expected redundancy, link speed, addressing, and reachability.
Start At The Physical Layer
Before changing software, confirm the physical path. Verify the correct server port, cable or DAC, transceiver type, patch-panel position, top-of-rack switch port, and labeling. Compare the rack elevation and cable map with OSDCTC.003: Structured Cabling and Patch Panels.
For fiber, match the approved optic type, wavelength, fiber type, connector type, polarity, and reach. For DACs or active electrical cables, verify that the cable is supported by both endpoints and rated for the intended speed. Do not assume a link light proves the correct path. A server can establish link on the wrong switch port or wrong VLAN.
Identify Every NIC Before Troubleshooting
On Linux, begin by listing the interfaces and mapping them to physical hardware. Interface names such as enp65s0f0np0 are predictable names derived from hardware topology, but they are not meaningful until you identify the actual adapter and port.
ip -br link
nmcli device status
lspci -nn | grep -i -E 'ethernet|network'
ethtool -i enp65s0f0np0
ethtool -i can show the NIC driver, firmware version, and PCI bus information. Use that information with the server inventory and BMC data from OSDCTC.006 to confirm you are working on the intended adapter.
Verify Link State, Speed, And Duplex
Red Hat documents ethtool as a primary verification tool for Ethernet link settings. A healthy output should show the expected speed, full duplex where applicable, and Link detected: yes. Red Hat also notes that both sides of an Ethernet link should use compatible auto-negotiation settings for optimal operation.
ethtool enp65s0f0np0Important fields include Speed, Duplex, Auto-negotiation, Port, and Link detected. A 100 Gb/s NIC that comes up at an unexpected lower rate is not a successful configuration and validation result even if basic ping works. Compare the negotiated rate with the server design, switch configuration, cable or optic capability, and switch-side port counters.
Network Direction — LACP fundamentals and dynamic EtherChannel behavior, useful when validating bonded server uplinks.
Read NIC Counters Before Blaming The Network
A link can remain up while traffic is unhealthy. NIC and driver counters can expose CRC errors, dropped packets, missed packets, overruns, pause events, resets, and other conditions that a simple connectivity test can miss.
ip -s link show enp65s0f0np0
ethtool -S enp65s0f0np0
Counter names are driver-specific, so do not diagnose from a single unfamiliar statistic. Establish a baseline, clear or record the current values according to site procedure, generate controlled traffic, then check which counters increase. A rapidly increasing receive-error counter points the investigation differently than a clean NIC with a switch-side VLAN mismatch.
Optics And Transceivers Need Their Own Checks
On supported hardware, ethtool -m can read transceiver EEPROM or diagnostic information. Depending on the module and driver, that may include vendor identification, wavelength, temperature, transmit power, and receive power.
ethtool -m enp65s0f0np0Do not treat a single optical power value as universally good or bad. Compare it with the transceiver specification, switch-side telemetry, fiber length, connector condition, and site standard. A low receive level can come from contamination, damaged fiber, excess loss, wrong optic pairing, or an upstream transmitter problem.
Understand Access Ports, Trunks, And VLAN Tags
A server-facing switch port may be configured as an untagged access port or as a trunk carrying one or more tagged VLANs. The Linux host configuration must match the switch design. If the switch expects VLAN tags but the host sends untagged frames, the physical link can be healthy while IP connectivity fails.
Red Hat documents VLAN creation through NetworkManager using nmcli. A representative example is:
nmcli connection add type vlan \
  con-name vlan120 \
  ifname bond0.120 \
  dev bond0 \
  id 120
This is an example, not a command to paste into an unknown production server. Confirm the approved VLAN ID, parent interface, addressing method, MTU, and change plan first. The switch and host must agree on tagging.
Network Direction — access-versus-trunk VLAN behavior and why the switch-side mode must match the host design.
Bonding Provides Redundancy Or Aggregation
Many servers use multiple physical NIC ports combined into a Linux bond. Red Hat Enterprise Linux supports several bonding modes. Two common designs are active-backup, where one port carries traffic while another remains available for failover, and 802.3ad, which uses Link Aggregation Control Protocol when the switch is configured for the same LACP relationship.
A representative 802.3ad creation command is:
nmcli connection add type bond \
  con-name bond0 \
  ifname bond0 \
  bond.options "mode=802.3ad,miimon=100"
The switch side must be intentionally configured to match. LACP is not simply “two cables plugged in.” Both server ports must belong to the intended aggregate, the switch ports must be in the corresponding port-channel or MLAG design, and hashing determines how flows are distributed.
Inspect the running Linux bond with:
cat /proc/net/bonding/bond0Verify the bond mode, active ports, MII status, aggregator information, partner state, and whether all expected members are actually participating. A bond can appear operational while one member is down or excluded.
LLDP Helps Prove Which Switch Port You Reached
Link Layer Discovery Protocol can advertise and learn neighbor information on a local Ethernet link. When LLDP is enabled and permitted by site policy, it can help validate that a server NIC is connected to the expected switch and port instead of relying only on cable labels.
Linux environments commonly use an LLDP daemon such as lldpd. A representative read-only command is:
lldpcli show neighborsCompare the discovered system name, port ID, VLAN information when advertised, and chassis information with the rack documentation. If LLDP is intentionally disabled for security or architecture reasons, use switch-side MAC tables, interface descriptions, and physical tracing instead.
Verify Addressing And Routing Separately From Link
Layer 1 and Layer 2 can be correct while Layer 3 is wrong. Confirm the assigned addresses, prefix length, gateway, routes, and active NetworkManager profile.
ip -br address
ip route
nmcli connection show --active
Do not assume that receiving an address proves the server is on the intended network. DHCP can succeed on the wrong VLAN. Compare the address and gateway with the deployment record, IPAM source, or approved build data.
MTU Mismatches Create Partial Failures
All devices in a path must support the frame size expected by the workload. A server configured for jumbo frames can communicate with small packets yet fail or perform poorly when larger frames cross a segment configured for a smaller MTU.
ip link show enp65s0f0np0
ip link show bond0
ip link show bond0.120
A controlled ping with the “do not fragment” behavior can help test an IP path, but interpret it carefully because firewalls and ICMP policy can affect results. The correct validation combines host MTU, switch configuration, expected path design, and application testing.
Test Connectivity In Layers
Do not jump directly to “the network is down.” Test from nearest dependency to farthest dependency:
- NIC is present and using the expected driver and firmware.
- Physical link is detected at the expected speed.
- Optic or cable is supported and healthy.
- Bond members are active if bonding is used.
- VLAN configuration matches the switch design.
- Correct IP address and prefix are present.
- Local gateway is reachable.
- Required routed destinations are reachable.
- DNS works when the application depends on names.
- Required service ports are reachable.
- Production monitoring sees the host from the expected network.
Use Packet Counters To Separate Physical And Logical Faults
If the link is up but the host cannot reach its gateway, watch receive and transmit counters while generating traffic. If transmit counters increase but receive remains flat, investigate the return path, VLAN, switch port, or peer. If neither counter moves, inspect the host configuration and whether traffic is actually being sent through that interface.
If packet capture is permitted by site policy, tcpdump can show ARP, neighbor discovery, DHCP, VLAN-tagged traffic, or ICMP directly. Capture only what is authorized and avoid collecting unnecessary production payload data.
A Link Light Is Only One Piece Of Evidence
One of the most common technician errors is treating link LEDs as proof of network readiness. A link LED usually proves only that two physical-layer devices established some form of link. It does not prove the correct switch, VLAN, IP, LACP state, MTU, route, DNS, firewall policy, or application path.
This is why server network configuration and validation should be documented as a chain of evidence rather than a single green light.
As data-center fabrics move toward ever-higher-speed Ethernet and optical interconnects, the physical details matter even more. This industry post highlights the continued shift toward optical data-center interconnects; treat it as industry discussion rather than a standards source.
Industry discussion — high-speed AI data-center links are increasingly optical, reinforcing the need for technicians to understand transceivers and fiber validation.
Practical Configuration And Validation Checklist
- Confirm the server asset, rack, U position, NIC port, cable ID, and expected switch port.
- Verify NIC hardware, driver, firmware, and interface naming.
- Check link detected, negotiated speed, duplex, and auto-negotiation state.
- Inspect optics, DACs, fiber cleanliness, polarity, and supported module types.
- Record NIC and switch counters before and after test traffic.
- Verify bond mode and every bond member when redundancy or aggregation is configured.
- Confirm LACP partner state when 802.3ad is used.
- Confirm VLAN tagging or untagged access behavior matches the network design.
- Use LLDP or approved switch-side tools to verify the physical neighbor.
- Confirm IP address, prefix, gateway, routes, DNS, and MTU.
- Test local gateway, routed destinations, and required service ports.
- Confirm production monitoring and inventory systems recognize the server.
- Document the final switch port, MAC addresses, IPs, bond members, VLANs, MTU, link speeds, and validation results.
Technician Pattern Recognition
- No link on one port: inspect cable or optic seating, compatibility, switch admin state, NIC firmware/driver, and physical path.
- Link is up but no gateway: inspect VLAN, IP prefix, gateway, bond state, switch port mode, and ARP or neighbor discovery.
- Bond works on one member only: inspect LACP membership, switch-side aggregate, cable path, and MII status.
- Traffic works until large transfers begin: inspect MTU, errors, FEC or optic health, congestion, and packet drops.
- Intermittent packet loss: compare NIC and switch counters, optic power, cable condition, buffer drops, and error trends.
- Server sees the wrong network: verify switch port, VLAN assignment, LLDP neighbor, DHCP source, and deployment record.
- Link speed is lower than design: check cable/optic capability, negotiation settings, switch configuration, and supported NIC modes.
Exercises
- Write a read-only Linux command sequence that identifies a NIC, verifies driver and firmware, checks link state, and records packet counters.
- Explain why a working link LED does not prove that the server is on the correct VLAN.
- A two-port 802.3ad bond shows one active member and one failed member. List the server-side and switch-side evidence you would collect.
- Describe how an MTU mismatch can create a partial network failure.
- Explain the difference between an untagged access-port design and a tagged VLAN trunk to a Linux host.
- Create a validation record for a new server containing rack location, NIC MAC addresses, switch ports, VLANs, IP addresses, MTU, bond mode, and link speed.
- A 100 Gb/s link is up but showing errors. Build a troubleshooting sequence that separates host, cable/optic, and switch causes.
Knowledge Check + Answers
- What does “Link detected: yes” prove? It proves the NIC reports physical link; it does not prove VLAN, IP, routing, or application correctness.
- What does
ethtool -ihelp identify? The NIC driver, firmware, and bus information. - What is 802.3ad used for? Link aggregation using LACP when the host and switch are configured for the same aggregate.
- Why inspect
/proc/net/bonding/bond0? It shows bond mode, member status, link monitoring, and partner or aggregator information. - What problem does a VLAN solve? It logically separates Layer-2 broadcast domains across shared Ethernet infrastructure.
- What is LLDP useful for during configuration and validation? It can help identify the directly connected switch and port when enabled.
- Why should NIC counters be recorded before and after traffic tests? The change in counters helps show whether packets, errors, or drops are occurring during the test.
- What must match for jumbo-frame operation? The required MTU must be supported consistently across the intended end-to-end path.
Prior Lessons And Primary References
- OSDCTC.007 — Server Provisioning and Deployment
- OSDCTC.006 — BMC and Out-of-Band Server Management
- OSDCTC.004 — Server Rack-and-Stack
- OSDCTC.003 — Structured Cabling and Patch Panels
- Red Hat Enterprise Linux 10 — Configuring a Network Bond
- Red Hat Enterprise Linux 9 — Configuring VLAN Tagging
- Red Hat Enterprise Linux — Configuring 802.3 Link Settings
- Red Hat Hardware Certification 2026 — Ethernet Validation
Elementary Conclusion
Server network configuration and validation is a layered proof process. Start with the exact physical path, identify the NIC, verify link state and negotiated speed, inspect optics and counters, prove bond and LACP membership, confirm VLAN behavior, validate addressing and routes, and then test the application path. A strong data-center technician does not stop when the link light turns green. The technician proves that the correct server is connected to the correct network with the expected redundancy, performance, and documented handoff state.
BitcoinVersus.Tech
Advertisement
BitcoinVersus.Tech publishes open technical education across data centers, networking, Linux, electrical systems, robotics, semiconductors, programming, and firmware.
Editor’s Note
Switch configuration, VLAN IDs, bond modes, LACP settings, MTU values, optics, NIC firmware, IP addressing, and production network changes are site- and vendor-specific. Follow approved change control, network standards, access permissions, and OEM documentation. The configuration commands in this lesson are examples and should not be applied blindly to production hosts.
We volunteer daily to help keep the information on this platform verifiably accurate. Support our independent research through the support options available on BitcoinVersus.Tech.
BitcoinVersus.tech is not a financial advisor. Content is provided for informational purposes.


Leave a Reply